
The most popular and comprehensive Open Source ECM platform
Let us know more


Hacking and exploits have unfortunately become common-place hazards of working with computers. The Department of Homeland Security (DHS) recently released the 2020 list of most dangerous software vulnerabilities, a list that they’re calling the Common Weakness Enumeration (CWE).
The CWE report explains that “these weaknesses are dangerous because they are often easy to find, exploit, and can allow adversaries to completely take over a system, steal data, or prevent an application from working.”
The ranking of the software vulnerabilities was determined based on a score that considered prevalence and severity (The Common Vulnerability Scoring System). The ranking gives an idea about which vulnerabilities are most commonly exploited by cybercriminals.
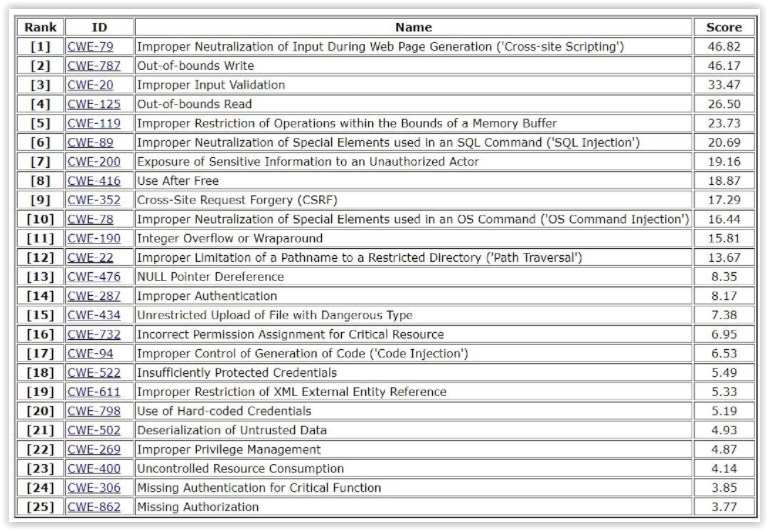
The number one software flaw is Cross Site Scripting. The injection of code into the client communication with the server can allow a cyberhacker to steal user identify, hijack accounts, steal credentials, access data, redirect content and introduce face content on the web site.
Steve Kosten, security consultant at cypress data defense, said that “XSS, cross-site scripting, is one of the most common security vulnerabilities found in web applications and it can cause severe damage if not mitigated in a timely manner… What’s worse is that victims of XSS attacks, both the user and the developer of the web application, often won’t be aware that they’re being attacked.”


